Our Digital Forensic Services
Digital Forensic and Incident Response (DFIR) Regulatory-Grade Threat Containment, Evidence Integrity, and Governance Frameworks
ASET™ At Rodasett, our governance-led methodology guarantees that every stage of our forensic investigation aligns with international compliance frameworks and legal evidentiary standards:
Rapid Breach Response. Court-Ready Forensics. Uncompromising Governance.
When a cyber incident threatens your systems, business continuity, and regulatory standing, every second counts.
Rodasett delivers 24/7 Digital Forensics & Incident Response (DFIR) backed by enterprise governance expertise. We contain active threats, trace root-cause vectors, and deliver legally sound forensic evidence to protect your operational integrity, insurance coverage, and board-level accountability.
- Governance-First Forensic Methodologies: Every evidence collection process adheres strictly to ISO/NIST chain-of-custody protocols. Our findings hold up in court, under insurance loss adjusters' scrutiny, and during formal audit reviews.
- ERP & Financial System Expertise: Unlike standard MSPs, Rodasett’s roots in enterprise SAP, financial controls, and SOX compliance give us specialized insight when investigating complex ledger tampering, privilege escalation, or unauthorized wire transfers.
- Insurance & Regulatory Alignment: We work directly with breach coaches, legal counsel, and insurance adjusters to help fulfill mandatory disclosure deadlines (e.g., GDPR 72-hour reporting, SEC/SOX disclosures)
60%
Over 60% of UK small businesses close their doors within six months of suffering a critical data breach.
30 %
Agencies operating without endpoint & identity controls face financial losses 4.3x higher during business email compromise (BEC) attacks
83%
82% of cyber breaches exploit human error, weak passwords, or unverified M365 cloud logins
11%
Only 11% of SMBs meet all baseline requirements required to qualify for full cyber insurance payouts
“The Intersection of Forensic Investigation & Regulatory Compliance. At Rodasett, every stage of our forensic investigation aligns with international compliance frameworks and legal evidentiary standards: ”
The Intersection of Forensic Investigation & Regulatory Compliance
Standard IT cleanup teams often wipe compromised servers immediately, inadvertently destroying volatile memory and forensic logs. This creates severe regulatory non-compliance, invalidates cyber insurance coverage, and leads to statutory penalties.
At Rodasett, our governance-led methodology guarantees that every stage of our forensic investigation aligns with international compliance frameworks and legal evidentiary standards:
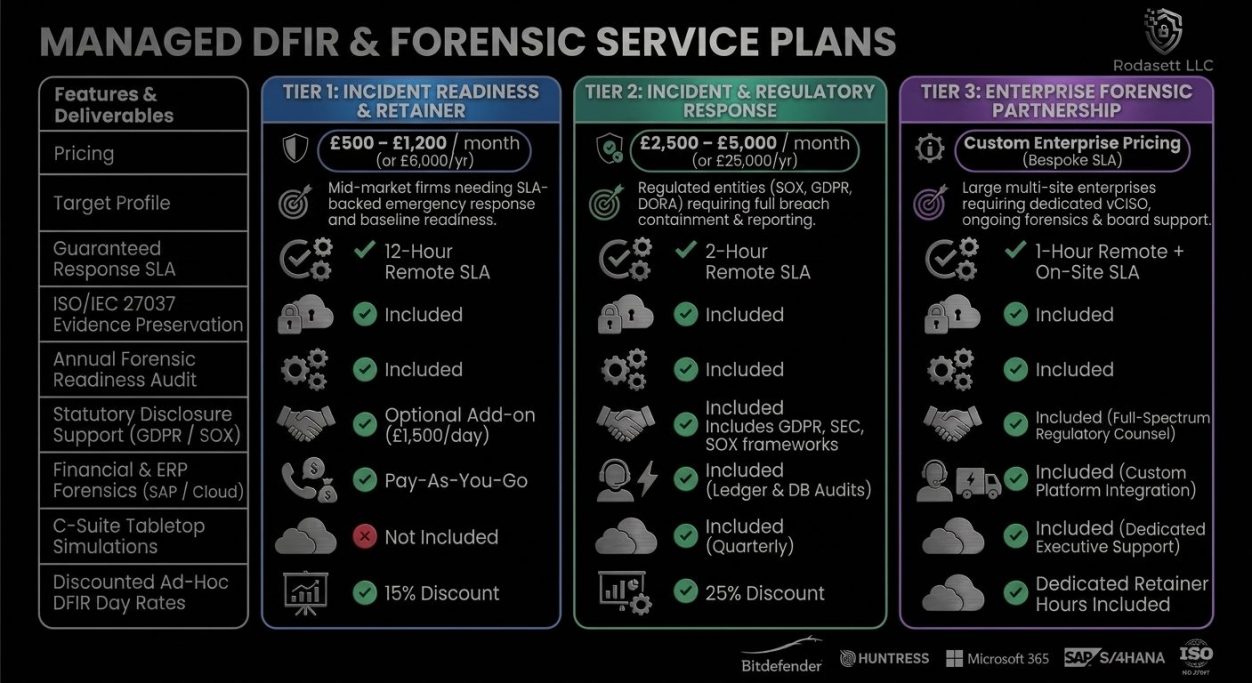
- Strict Chain of Custody: All evidence collection follows ISO/IEC 27037 guidelines, ensuring forensic artifacts remain admissible in court and during regulatory audits.
- Statutory Disclosure Support: Precise data exfiltration analysis to establish whether Personal Identifiable Information (PII) or material financial data was impacted, satisfying mandatory GDPR 72-hour reporting and SEC/SOX material breach notification deadlines.
- Financial & ERP Audit Trails: Specialized forensic capabilities across core enterprise architectures—including SAP S/4HANA, cloud databases, and financial ledgers—to trace unauthorized privilege escalation, ledger alterations, or wire fraud.
Compliance-Centric DFIR Services
1. Regulatory-Grade Emergency Incident Response
Rapid threat containment paired with mandatory compliance record-keeping.
- 24/7 Containment & Isolation: Rapid isolation of compromised endpoints, cloud tenants, and network segments to halt active ransomware execution or unauthorized exfiltration.
- Volatile Memory & Log Preservation: Instant capture of RAM, active network connections, and system logs to construct a verifiable timeline before threat actors can purge audit trails.
- Eradication with Governance Controls: Safe eviction of persistent backdoors and unauthorized identities without compromising regulatory evidence.
2. Forensic Root-Cause & Impact Analysis
Determining the precise scope of exposure for legal and regulatory authorities.
- Scope-of-Breach Verification: Definitive technical analysis to verify if sensitive data was actually viewed, acquired, or exfiltrated, preventing unnecessary and costly mass-breach disclosures.
- Malware & Artifact Deconstruction: Reconstructing custom payloads and command-and-control communication channels to supply technical Indicators of Compromise (IOCs) to oversight bodies.
- Cloud & Infrastructure Timeline Reconstruction: Comprehensive analysis across AWS, Azure, Microsoft 365, and on-premises domain controllers to map every action taken by threat actors.
3. Insider Fraud, Privilege Abuse & Internal Investigations
Confidential forensic analysis for internal audit teams, board members, and legal counsel.
- ERP & Financial System Forensics: Tracing unauthorized transactions, ledger tampering, and administrative access violations across critical financial applications.
- Internal Misconduct Analytics: Forensically sound imaging and examination of employee hardware, email archives, and cloud storage to investigate intellectual property theft or fraud.
- Court-Ready Expert Reports: Delivering jargon-free executive findings designed for breach coaches, external auditors, law enforcement, and judicial proceedings.
4. Proactive Forensic Readiness & Retainers
Building defensible compliance frameworks before an incident occurs.
- SLA-Backed Emergency Retainers: Guaranteed 1-to-2-hour emergency response times backed by dedicated senior forensic investigators.
- Forensic Readiness Audits: Evaluating log retention settings, SIEM telemetry, and system visibility to guarantee your environment will generate compliant, defensible evidence during a breach.
- C-Suite & Board Tabletop Simulations: Simulating high-consequence cyber scenarios (e.g., ransomware, supply-chain compromise) to test executive decision-making, legal workflows, and regulatory reporting chains.